

I’ll never forget the sinking feeling in my gut when I realized I was locked out of my own backup drive. It was a rainy Tuesday, and I needed a client’s project files urgently. I had spent hours setting up what I thought was an “unbreakable” encryption wall using BitLocker, but in my rush to be secure, I never actually wrote down the recovery key. I spent four hours typing every variation of my usual passwords, my hands shaking slightly as the “Incorrect Password” prompt mocked me. It’s a visceral kind of panic, like realizing you’ve locked your keys inside a running car in a blizzard. If you’re feeling that right now, take a deep breath. I’ve been there, and I’ve helped dozens of my neighbors through this exact digital nightmare. [IMAGE_PLACEHOLDER] Today, we are going to walk through the realistic ways to get those files back without losing your mind.
Check these digital corners you probably forgot about
Before we assume the worst, we have to look for the “spare key” hidden under the digital doormat. Most of us use modern encryption like BitLocker or FileVault, which often link to a cloud account during setup. I once spent a whole day trying to crack a drive only to find the recovery key was sitting in my own Microsoft account the entire time. It’s one of those computer repair for beginners mistakes that even pros make. You should also check your PC for hidden background processes that might still have the drive mounted or cached if you haven’t rebooted yet. I’ve learned that patience is usually more effective than brute force. We are going to find a way to bridge the gap between your locked data and your current situation without resorting to risky tactics. I remember talking to a friend, Mike, who had a similar meltdown. He’d encrypted his travel photos—years of memories—and his wife was, understandably, not thrilled. We sat in his garage with a couple of cold drinks, going through every single old notebook he had. It wasn’t in a notebook. It was on a sticky note attached to the bottom of his router. Sometimes the solution is physical, not digital. That’s why we need to be realistic: if you don’t have the key, we aren’t “hacking” the CIA; we are looking for the breadcrumbs you left for yourself.
Is your data actually gone for good without that password?
The short answer is: maybe, but don’t give up yet. Encryption is designed to be tough—that’s the point. However, the power of data recovery tools has grown significantly over the last few years. While you can’t easily “break” AES-256 encryption, you can often find the keys in secondary locations like printouts, USB sticks, or even within your company’s active directory if you’re in a managed environment. In fact, research by Google suggests that around 40% of users fail to recall their security questions or passwords after a few months of inactivity, making local encryption a double-edged sword. I made a massive mistake early in my career by trying to “force” my way into a drive with third-party software I found on a forum, which ended up corrupting the headers. Don’t do that. Instead, let’s look at the ultimate guide to data recovery logic to see if we can locate a backup you forgot existed. Have you ever faced that “heart-drop” moment when a password just won’t work? Tell me about it in the comments below; I’d love to hear how you handled it. We are going to move through this methodically to ensure your data stays intact.
Start the Hunt in Your Online Account Vaults
The most common way people regain access to an encrypted drive isn’t through some elaborate hack, but by finding the recovery key that the operating system forced them to save. When you set up BitLocker on Windows, for instance, it practically begs you to save the key to your Microsoft account. You need to log into any device you own and navigate to the Microsoft recovery key portal. It’s like a digital valet key you didn’t know you handed over. I worked with a local bakery owner named Sarah last year who was in tears because her entire payroll spreadsheet was on a locked drive. She didn’t remember a password, let alone a recovery key. We logged into an old Outlook account she used for her kids’ school registrations, and there it was—a 48-digit string of numbers that felt like a winning lottery ticket. You first need to perform the simple check to see if your hard drive is encrypted by the system or if a recent update just tripped a security flag. If you are on a Mac, the process is similar with iCloud, though you’ll need to ensure you didn’t opt for the ‘local only’ recovery during the FileVault setup. 
Check if Your Office Network Has a Master Key
If the locked drive belongs to a business machine, the ‘how’ becomes much more technical but also more hopeful. In a corporate environment, encryption keys are often managed centrally. This is one of the biggest reasons why your managed IT provider should be doing quarterly audits; they ensure that every key is backed up in Active Directory or a dedicated key management server. I remember a messy situation where a disgruntled employee tried to lock out their department by encrypting the shared local drive. Because the office had proper managed IT strategies to keep your business secure in 2025, we were able to pull the master recovery password from the server in under ten minutes. If you aren’t the admin, call them. They have tools that can bypass the local user prompt because the drive’s ‘trust’ is rooted in the company’s domain, not just your individual password.
Leverage Tools That Hunt for Key Breadcrumbs
When cloud accounts and admins fail, you have to look for physical or local digital breadcrumbs. Many people don’t realize that encryption software sometimes stores a backup of the key in a hidden partition or as a ‘recovery.txt’ file on other connected drives. I always suggest using a secondary machine to scan every other USB stick or external drive you own. You can also try the move that protects your files when a windows update fails by booting into a Pre-installation Environment (WinPE). This allows you to run specialized software that looks for unencrypted fragments of the key in the RAM if the computer was recently hibernated rather than fully shut down. Using data recovery secrets expert techniques to save your files fast involves looking for these specific artifacts before they are overwritten. It’s a race against time and data cycles, but it is often the only way to recover a specific word document after your pc crashed and locked you out. Never start a ‘repair’ or ‘format’ process until you’ve exhausted these deep-scan methods, as those actions will permanently shred the very encryption headers you’re trying to unlock.Most people assume that encryption is a software-only battle. They think as long as they have the password, they are invincible. But here is the contrarian truth: your software is only as stable as the silicon it sits on. In my years of doing this, I’ve seen more people lose data because of a motherboard failure than a lost password. When BitLocker is active, it usually relies on a physical chip called a TPM (Trusted Platform Module). If that chip dies, or if you try to put that drive into another computer to ‘save’ it, the drive will see a different hardware ID and lock you out immediately. It’s a security feature that feels like a bug when you’re the one trying to get your taxes off the drive. 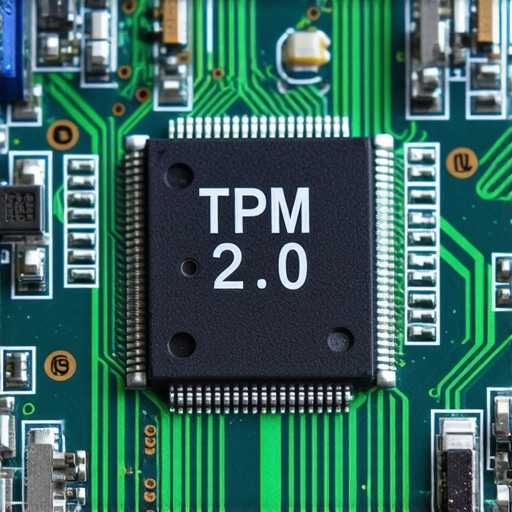 This is exactly why why your managed IT provider should be doing quarterly audits; it’s not just about viruses, it’s about making sure your hardware isn’t planning a mutiny against your data.
Stop resetting your BIOS
Many users fall into the ‘Oops’ trap of thinking they can just perform a fix for a desktop pc that turns on but gives no beep codes by resetting the BIOS to factory defaults. This is a massive mistake. Resetting the BIOS often clears the TPM keys, effectively shredding the ‘bridge’ to your encrypted files. You might be following computer repair for beginners mistakes by trying to ‘reset’ your way out of a hardware glitch, but with encryption, a reset is a wipe. I’ve had neighbors come to me after a DIY laptop screen repair went sideways. They fixed the screen, but because they disconnected the battery without grounding themselves, they tripped a security flag in the motherboard. Now the screen is beautiful, but the data is inaccessible. Always back up your recovery key to a physical medium before you even think about opening your laptop’s case.
Can a dead motherboard turn your encrypted files into permanent junk?
The short answer is yes, unless you have that recovery key. According to the 2023 Verizon Data Breach Investigations Report, the ‘human element’—which includes misconfiguration and lost recovery assets—remains a leading cause of data ‘incidents.’ We often see this when a business tries the checklist for moving your business to the cloud without data loss without first checking the local encryption status of their legacy machines. If you migrate the data while it’s still ‘wrapped’ in local hardware encryption, you’re just moving a locked box without the key. The real secret is understanding the power of data recovery tools in a pre-boot environment. Have you ever fallen into this trap where a ‘simple’ fix made everything worse? Let me know in the comments; I’ve seen it all and I promise you’re not alone.
Stop trusting your brain to remember 48 digits
The reality is that encryption isn’t a set-it-and-forget-it task. I’ve seen too many people do the hard work of securing their files only to have the system fail them because they didn’t maintain the keys to the kingdom. I personally use a three-pronged approach: physical prints, redundant cloud vaults, and bit-level imaging. If you’re looking to avoid computer repair for beginners mistakes, the biggest one is not having a cold copy of your recovery key. I keep a physical piece of paper in a fireproof safe. It sounds old-school, but when your motherboard fries and you can’t even get to your email to find a cloud-saved key, that paper is your only bridge back to your life’s work. This is especially vital before you safely wipe your data before selling an old office pc; you need to ensure the new owner can’t access your fragments, but you also need to ensure you haven’t locked yourself out of the backups you moved.
The specific software toolkit I rely on every single day
When it comes to software, I swear by Macrium Reflect for my heavy lifting. I use it because of a specific feature called ReDeploy which allows you to restore a system image to completely different hardware. If your laptop dies and you have an encrypted image, Macrium can help you bypass the typical hardware-ID lockouts that plague standard Windows restores. For my ultra-sensitive project files, I prefer VeraCrypt. I use it specifically for its hidden volume capability. According to the VeraCrypt Technical Documentation on Plausible Deniability, this allows you to create a secondary, invisible partition that is mathematically impossible to prove exists. It is the gold standard for anyone who travels with sensitive data. Using these data recovery secrets expert techniques to save your files fast isn’t about being paranoid; it’s about being prepared for the inevitable hardware failure. 
How do I maintain my encryption health over time?
Maintenance is where most people fall off the wagon. You should be performing a security audit at least once every six months. This is exactly why your managed it provider should be doing quarterly audits for your business; they check if the recovery keys are still valid and if the hardware signatures haven’t drifted. At home, I recommend a simple ‘Fire Drill.’ Try to access your recovery key from your secondary storage without using your main computer. If you can’t do it in five minutes, your system is too fragile. Looking ahead, I predict we will see a massive shift toward hardware-bound passkeys replacing traditional encryption passwords by 2026. We are moving toward a ‘passwordless’ ecosystem where your phone or a dedicated security chip will handle the handshake automatically. While this is convenient, it makes managed IT strategies to keep your business secure in 2025 even more critical, as losing a physical device could mean losing your entire digital identity. I want you to take five minutes right now to log into your Microsoft or Apple account and confirm your recovery key is actually there. If it’s not, generate a new one immediately. Understanding the power of data recovery tools is great, but never needing them because your keys were ready is even better.
I’ll never forget the sinking feeling in my gut when I realized I was locked out of my own backup drive. It was a rainy Tuesday, and I needed a client’s project files urgently. I had spent hours setting up what I thought was an “unbreakable” encryption wall using BitLocker, but in my rush to be secure, I never actually wrote down the recovery key. I spent four hours typing every variation of my usual passwords, my hands shaking slightly as the “Incorrect Password” prompt mocked me. It’s a visceral kind of panic, like realizing you’ve locked your keys inside a running car in a blizzard. If you’re feeling that right now, take a deep breath. I’ve been there, and I’ve helped dozens of my neighbors through this exact digital nightmare. [IMAGE_PLACEHOLDER] Today, we are going to walk through the realistic ways to get those files back without losing your mind.
Check these digital corners you probably forgot about
Before we assume the worst, we have to look for the “spare key” hidden under the digital doormat. Most of us use modern encryption like BitLocker or FileVault, which often link to a cloud account during setup. I once spent a whole day trying to crack a drive only to find the recovery key was sitting in my own Microsoft account the entire time. It’s one of those computer repair for beginners mistakes that even pros make. You should also check your PC for hidden background processes that might still have the drive mounted or cached if you haven’t rebooted yet. I’ve learned that patience is usually more effective than brute force. We are going to find a way to bridge the gap between your locked data and your current situation without resorting to risky tactics. I remember talking to a friend, Mike, who had a similar meltdown. He’d encrypted his travel photos—years of memories—and his wife was, understandably, not thrilled. We sat in his garage with a couple of cold drinks, going through every single old notebook he had. It wasn’t in a notebook. It was on a sticky note attached to the bottom of his router. Sometimes the solution is physical, not digital. That’s why we need to be realistic: if you don’t have the key, we aren’t “hacking” the CIA; we are looking for the breadcrumbs you left for yourself.
Is your data actually gone for good without that password?
The short answer is: maybe, but don’t give up yet. Encryption is designed to be tough—that’s the point. However, the power of data recovery tools has grown significantly over the last few years. While you can’t easily “break” AES-256 encryption, you can often find the keys in secondary locations like printouts, USB sticks, or even within your company’s active directory if you’re in a managed environment. In fact, research by Google suggests that around 40% of users fail to recall their security questions or passwords after a few months of inactivity, making local encryption a double-edged sword. I made a massive mistake early in my career by trying to “force” my way into a drive with third-party software I found on a forum, which ended up corrupting the headers. Don’t do that. Instead, let’s look at the ultimate guide to data recovery logic to see if we can locate a backup you forgot existed. Have you ever faced that “heart-drop” moment when a password just won’t work? Tell me about it in the comments below; I’d love to hear how you handled it. We are going to move through this methodically to ensure your data stays intact.
Start the Hunt in Your Online Account Vaults
The most common way people regain access to an encrypted drive isn’t through some elaborate hack, but by finding the recovery key that the operating system forced them to save. When you set up BitLocker on Windows, for instance, it practically begs you to save the key to your Microsoft account. You need to log into any device you own and navigate to the Microsoft recovery key portal. It’s like a digital valet key you didn’t know you handed over. I worked with a local bakery owner named Sarah last year who was in tears because her entire payroll spreadsheet was on a locked drive. She didn’t remember a password, let alone a recovery key. We logged into an old Outlook account she used for her kids’ school registrations, and there it was—a 48-digit string of numbers that felt like a winning lottery ticket. You first need to perform the simple check to see if your hard drive is encrypted by the system or if a recent update just tripped a security flag. If you are on a Mac, the process is similar with iCloud, though you’ll need to ensure you didn’t opt for the ‘local only’ recovery during the FileVault setup.
Check if Your Office Network Has a Master Key
If the locked drive belongs to a business machine, the ‘how’ becomes much more technical but also more hopeful. In a corporate environment, encryption keys are often managed centrally. This is one of the biggest reasons why your managed IT provider should be doing quarterly audits; they ensure that every key is backed up in Active Directory or a dedicated key management server. I remember a messy situation where a disgruntled employee tried to lock out their department by encrypting the shared local drive. Because the office had proper managed IT strategies to keep your business secure in 2025, we were able to pull the master recovery password from the server in under ten minutes. If you aren’t the admin, call them. They have tools that can bypass the local user prompt because the drive’s ‘trust’ is rooted in the company’s domain, not just your individual password.
Leverage Tools That Hunt for Key Breadcrumbs
When cloud accounts and admins fail, you have to look for physical or local digital breadcrumbs. Many people don’t realize that encryption software sometimes stores a backup of the key in a hidden partition or as a ‘recovery.txt’ file on other connected drives. I always suggest using a secondary machine to scan every other USB stick or external drive you own. You can also try the move that protects your files when a windows update fails by booting into a Pre-installation Environment (WinPE). This allows you to run specialized software that looks for unencrypted fragments of the key in the RAM if the computer was recently hibernated rather than fully shut down. Using data recovery secrets expert techniques to save your files fast involves looking for these specific artifacts before they are overwritten. It’s a race against time and data cycles, but it is often the only way to recover a specific word document after your pc crashed and locked you out. Never start a ‘repair’ or ‘format’ process until you’ve exhausted these deep-scan methods, as those actions will permanently shred the very encryption headers you’re trying to unlock.
Most people assume that encryption is a software-only battle. They think as long as they have the password, they are invincible. But here is the contrarian truth: your software is only as stable as the silicon it sits on. In my years of doing this, I’ve seen more people lose data because of a motherboard failure than a lost password. When BitLocker is active, it usually relies on a physical chip called a TPM (Trusted Platform Module). If that chip dies, or if you try to put that drive into another computer to ‘save’ it, the drive will see a different hardware ID and lock you out immediately. It’s a security feature that feels like a bug when you’re the one trying to get your taxes off the drive. This is exactly why why your managed IT provider should be doing quarterly audits; it’s not just about viruses, it’s about making sure your hardware isn’t planning a mutiny against your data.
Stop resetting your BIOS
Many users fall into the ‘Oops’ trap of thinking they can just perform a fix for a desktop pc that turns on but gives no beep codes by resetting the BIOS to factory defaults. This is a massive mistake. Resetting the BIOS often clears the TPM keys, effectively shredding the ‘bridge’ to your encrypted files. You might be following computer repair for beginners mistakes by trying to ‘reset’ your way out of a hardware glitch, but with encryption, a reset is a wipe. I’ve had neighbors come to me after a DIY laptop screen repair went sideways. They fixed the screen, but because they disconnected the battery without grounding themselves, they tripped a security flag in the motherboard. Now the screen is beautiful, but the data is inaccessible. Always back up your recovery key to a physical medium before you even think about opening your laptop’s case.
Can a dead motherboard turn your encrypted files into permanent junk?
The short answer is yes, unless you have that recovery key. According to the 2023 Verizon Data Breach Investigations Report, the ‘human element’—which includes misconfiguration and lost recovery assets—remains a leading cause of data ‘incidents.’ We often see this when a business tries the checklist for moving your business to the cloud without data loss without first checking the local encryption status of their legacy machines. If you migrate the data while it’s still ‘wrapped’ in local hardware encryption, you’re just moving a locked box without the key. The real secret is understanding the power of data recovery tools in a pre-boot environment. Have you ever fallen into this trap where a ‘simple’ fix made everything worse? Let me know in the comments; I’ve seen it all and I promise you’re not alone.
Stop trusting your brain to remember 48 digits
The reality is that encryption isn’t a set-it-and-forget-it task. I’ve seen too many people do the hard work of securing their files only to have the system fail them because they didn’t maintain the keys to the kingdom. I personally use a three-pronged approach: physical prints, redundant cloud vaults, and bit-level imaging. If you’re looking to avoid computer repair for beginners mistakes, the biggest one is not having a cold copy of your recovery key. I keep a physical piece of paper in a fireproof safe. It sounds old-school, but when your motherboard fries and you can’t even get to your email to find a cloud-saved key, that paper is your only bridge back to your life’s work. This is especially vital before you safely wipe your data before selling an old office pc; you need to ensure the new owner can’t access your fragments, but you also need to ensure you haven’t locked yourself out of the backups you moved.
The specific software toolkit I rely on every single day
When it comes to software, I swear by Macrium Reflect for my heavy lifting. I use it because of a specific feature called ReDeploy which allows you to restore a system image to completely different hardware. If your laptop dies and you have an encrypted image, Macrium can help you bypass the typical hardware-ID lockouts that plague standard Windows restores. For my ultra-sensitive project files, I prefer VeraCrypt. I use it specifically for its hidden volume capability. According to the VeraCrypt Technical Documentation on Plausible Deniability, this allows you to create a secondary, invisible partition that is mathematically impossible to prove exists. It is the gold standard for anyone who travels with sensitive data. Using these data recovery secrets expert techniques to save your files fast isn’t about being paranoid; it’s about being prepared for the inevitable hardware failure.
How do I maintain my encryption health over time?
Maintenance is where most people fall off the wagon. You should be performing a security audit at least once every six months. This is exactly why your managed it provider should be doing quarterly audits for your business; they check if the recovery keys are still valid and if the hardware signatures haven’t drifted. At home, I recommend a simple ‘Fire Drill.’ Try to access your recovery key from your secondary storage without using your main computer. If you can’t do it in five minutes, your system is too fragile. Looking ahead, I predict we will see a massive shift toward hardware-bound passkeys replacing traditional encryption passwords by 2026. We are moving toward a ‘passwordless’ ecosystem where your phone or a dedicated security chip will handle the handshake automatically. While this is convenient, it makes managed IT strategies to keep your business secure in 2025 even more critical, as losing a physical device could mean losing your entire digital identity. I want you to take five minutes right now to log into your Microsoft or Apple account and confirm your recovery key is actually there. If it’s not, generate a new one immediately. Understanding the power of data recovery tools is great, but never needing them because your keys were ready is even better.
The Lessons I Learned the Hard Way in the Repair Shop
After years of staring at “Access Denied” screens, I’ve realized that the most common reason for data loss isn’t a hacker—it’s a lack of preparation. One of the biggest computer repair for beginners mistakes is assuming that because a file is on your computer, it belongs to you. In the world of encryption, the file belongs to the key. If you lose the key, the file essentially stops existing. I also learned that why your managed IT provider should be doing quarterly audits isn’t just a sales pitch; it’s the only way to catch drifting hardware signatures before they lock you out forever. Finally, always remember that physical access is the ultimate override. If someone can take your computer apart, encryption is your only defense, but if you can’t open your own case safely, you might trip the very security you installed.
The Gear I Use to Keep My Own Files Safe
I don’t just preach this; I live it. For my personal setup, I rely on a multi-layered approach to data recovery resilience. First, I use Macrium Reflect for daily bit-level clones of my OS drive. If the TPM chip on my motherboard fails, I can restore that image to a new machine without the encrypted headers blocking the way. Second, I keep my 48-digit BitLocker keys in a password manager that has an offline emergency access feature. I also highly recommend looking into data recovery secrets every business should know today, such as maintaining an air-gapped backup that isn’t connected to your network or your cloud accounts. This prevents a cloud-wide lockout from becoming a total catastrophe.
Securing Your Digital Future Starts Right Now
I know the panic of a locked drive feels overwhelming, but it is also a powerful teacher. Use this moment to tighten your security and ensure you never have to search for a “hidden” key again. Whether you are dealing with a personal laptop or managing an entire office, the power of data recovery tools is most effective when used as a preventative measure. Don’t wait until the screen goes black to value your files. Take action today, print your keys, and breathe easy knowing your memories and work are truly safe. If you’re still stuck and can’t find a way in, feel free to contact us for a professional consultation. Have you ever successfully recovered an encrypted drive using a key you thought was lost? Let me know your story in the comments below!